Quick Answer: Hackers redirect payments by getting into a real Microsoft 365 mailbox, yours or a vendor's, reading invoice conversations, and then sending "updated" bank details at the exact moment a payment is due. The strongest defense is one simple rule: no change to payment instructions is ever accepted by email alone. Confirm it by phone, using a number you already had on file.
This is one of the main email threats BridgeNet's cybersecurity team helps businesses guard against.
How does a payment redirect scam actually work?
It almost never starts with a fake invoice out of nowhere. It starts with patience.
- They get in. An employee or vendor signs in to a fake Microsoft 365 login page, and the attacker now has access to a real mailbox.
- They watch. They read old threads to learn who pays whom, how invoices are worded, and when payments go out.
- They hide. They set up inbox rules so replies about payments get moved out of sight, where the real owner won't notice them.
- They wait. When a large invoice or a closing payment comes up, they step into the conversation.
- They redirect. They send a short, polite note: the bank account has changed, please use the attached details for this payment.
By the time anyone notices, the money has usually moved on from the first account it landed in.
Why do these emails look so real?
Because in many cases, they are real.
If the attacker is inside the actual mailbox, the email comes from the actual address. It shows up in the existing thread. The signature, the tone, and the invoice numbers all match, because they were copied from the last ten messages.
Spam filters don't catch it. Nothing about the message is technically suspicious.
In other cases, the attacker uses a lookalike domain. One extra letter, a swapped "rn" for "m," or a .co instead of .com. On a phone screen, those are easy to miss.
Either way, the email itself is not where you catch this. The process around it is.
Is it your account or your vendor's that's compromised?
It can be either, and the damage looks different.
If a vendor's mailbox is compromised, your business receives the fake instructions. You pay the attacker, and your vendor is still waiting to be paid.
If your mailbox is compromised, your customers receive fake instructions that appear to come from you. They pay the attacker, believing they paid your invoice.
That second scenario is a hard conversation to have with a customer. It is one reason companies that send a lot of invoices, like construction firms billing on draws or manufacturers with large purchase orders, need to protect their own mailboxes, not just watch for incoming fraud.
What are the red flags in a payment change request?
Any one of these is a reason to stop and call:
- A request to change bank details, especially close to a due date
- Urgency: "please process today," "before the wire cutoff," "the old account is frozen"
- A new reason not to call: "I'm traveling," "I'm in meetings all day, just email me"
- A different domain, even slightly, from earlier emails in the thread
- Attachments with banking details instead of an updated W-9 or vendor form through your normal process
- A change in tone from someone you've worked with for years
None of these prove fraud. All of them justify a two-minute phone call.
How do you stop a payment redirect before it happens?
The best defenses are part process, part technology.
On the process side:
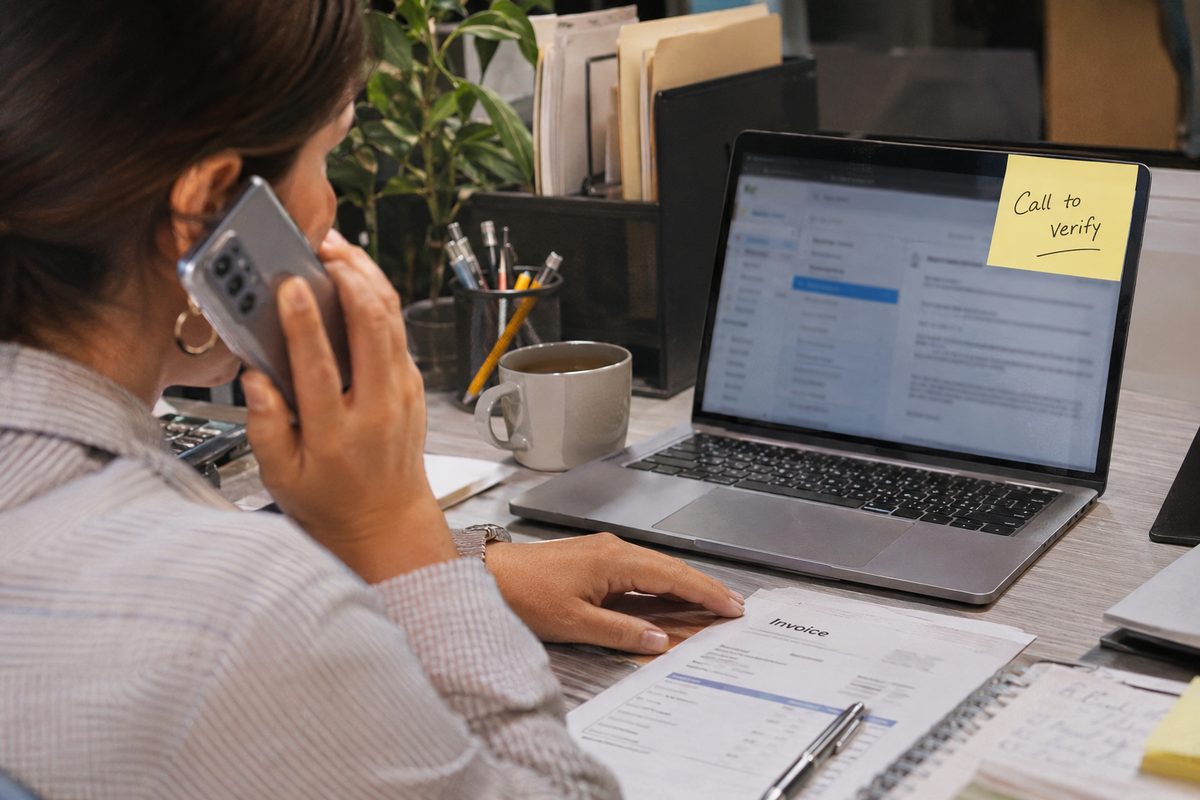
- Call to confirm every payment change. Use the number from your vendor file or the original contract, never the one in the email asking for the change.
- Require two people for changes. One person enters new bank details, a second person approves them.
- Train the people who pay bills. Your bookkeeper and office manager are the real targets here. Show them what these requests look like.
On the technology side:
- Turn on multi-factor authentication for every Microsoft 365 account, especially accounting and leadership.
- Block automatic forwarding of email to outside addresses, unless there's a business reason for it.
- Turn on alerts for suspicious sign-ins and new inbox rules, and make sure someone actually reviews them.
- Set up email authentication (SPF, DKIM, and DMARC) so others can't easily send mail pretending to be your domain.
What should you do if a payment already went to the wrong account?
Act within the hour, not the week.
- Call your bank immediately and ask them to recall the wire or payment. The faster they contact the receiving bank, the better the odds.
- File a report with the FBI's Internet Crime Complaint Center at ic3.gov.
- Lock down the mailbox that was used, whether it was yours or the vendor's. Reset the password, sign out all sessions, and remove any rules or forwarding.
- Call your cyber insurance carrier if you have one. Many policies have specific reporting steps.
Recovery is never guaranteed. Speed is the one factor you control.
Want a second set of eyes on how your business handles payment changes and email security? BridgeNet's team will review your Microsoft 365 settings and walk through your payment approval process with you. Call 985-635-4380 or schedule a free cybersecurity assessment.